SHA-512/256 generator
Create SHA-512/256 hashes from any string input using our SHA-512/256 generator tool for secure data encryption.
SHA-512/256 generator is a free tool that creates a SHA-512/256 hash from any string input.
What is SHA-512/256?
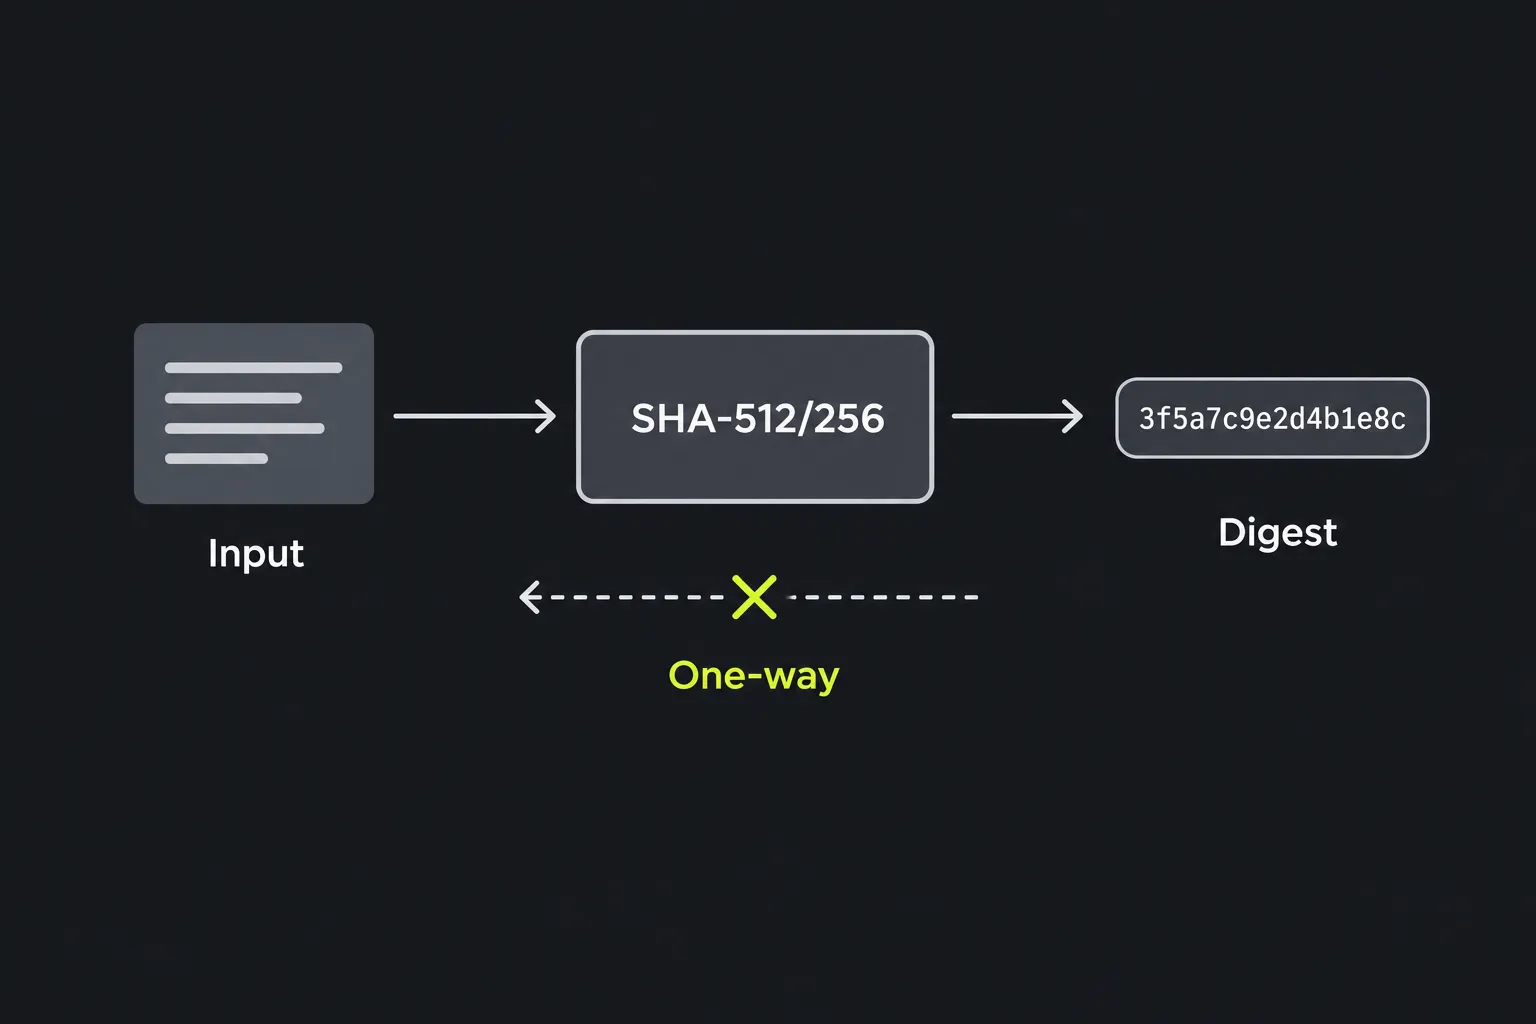
SHA-512/256 is a cryptographic hash algorithm that produces a fixed-length, 256-bit fingerprint of supplied data. SHA-512/256 works in one direction: the same input produces the same 256-bit digest, while even a small change normally produces a substantially different result. The SHA-512/256 hash function itself does not use a key and has no decryption step.
SHA-512/256 belongs to the SHA-2 family, designed by the U.S. National Security Agency and first standardized by NIST in 2002. The SHA-512/256 variant was added to FIPS 180-4 in 2012. It uses SHA-512's 64-bit internal design with a distinct initial value, then returns a 256-bit digest. It is therefore not simply SHA-512 shortened to 256 bits.
The digest is 32 bytes, usually written as 64 hexadecimal characters. SHA-512/256 remains suitable for cryptographic hashing, with no known practical collision or preimage attack. Its expected collision resistance is about 128 bits, while its preimage resistance is about 256 bits.
How do I generate a SHA-512/256 hash?
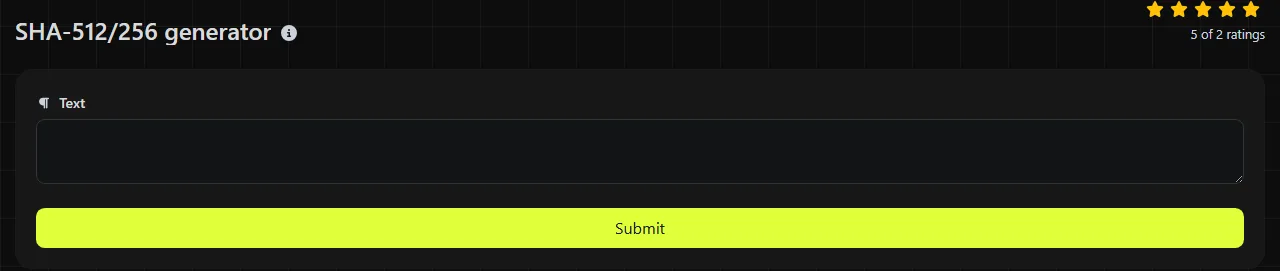
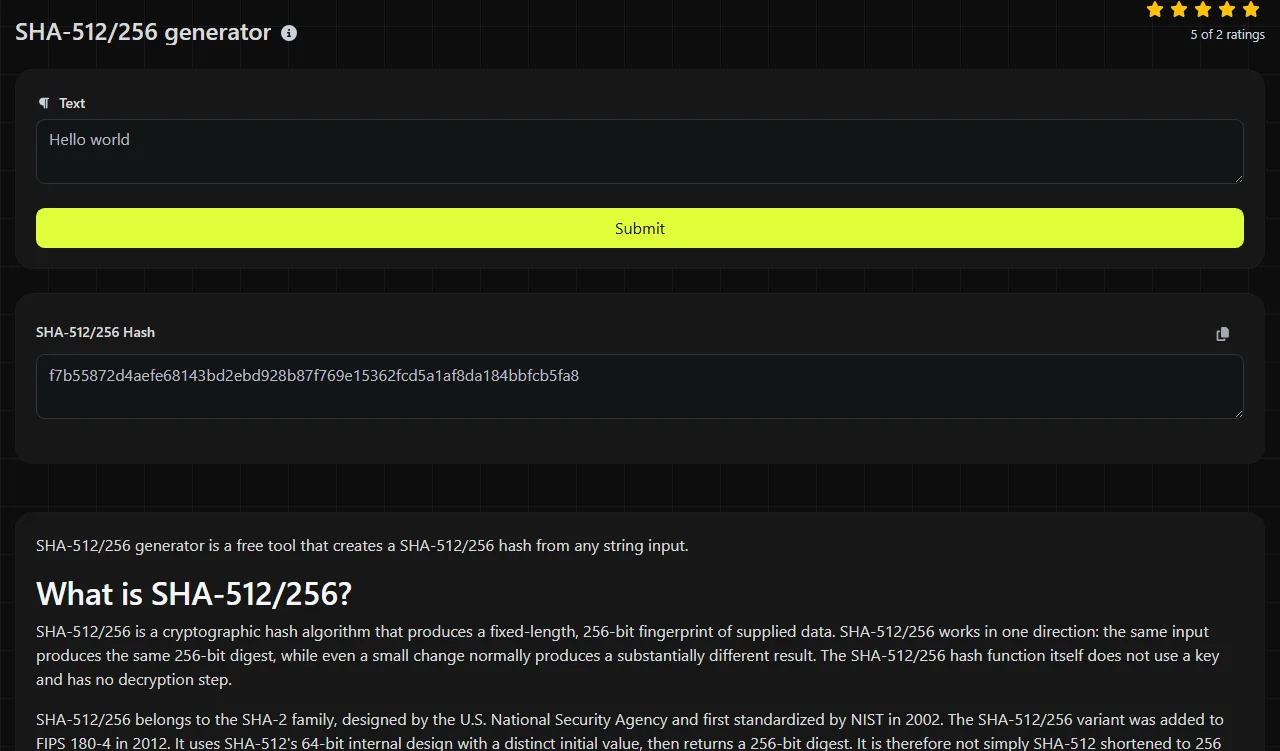
Enter the exact string you want to hash and use the value shown in the SHA-512/256 Hash result field. The calculation runs on the server. Your input is sent to the server over HTTPS and is not stored.
Copy the entire 64-character digest rather than a shortened portion unless a specification explicitly requires truncation. For example, hashing the string invoice-1042 produces a 256-bit value displayed as 64 hexadecimal characters. Hashing Invoice-1042 produces a different value because letter case is part of the input.
Carefully check the string entered in this SHA-512/256 generator before relying on the result. These are all different byte sequences and therefore have different hashes:
- report
- Report
- report with a trailing space
- report. with punctuation
- report followed by a hidden line break
Can SHA-512/256 be decrypted or reversed?
No, a SHA-512/256 digest cannot be decrypted because hashing is not encryption. The digest does not contain a recoverable copy of the original string, and there is no key that reverses the calculation.
An attacker can still use SHA-512/256 to hash possible inputs and compare the results. Short, common, or predictable strings are therefore vulnerable to dictionary and brute-force searches even though the algorithm itself is not reversed. This is one reason a plain SHA-512/256 hash must not be used to store passwords. For password storage, use a deliberately slow, salted password-hashing scheme such as Argon2id, bcrypt, or scrypt instead of this tool's plain SHA-512/256 output.
Where is SHA-512/256 still used?
SHA-512/256 is used when a 256-bit digest is required and software supports this specific SHA-2 variant. Its SHA-512-based internals can suit implementations designed for 64-bit processing, but actual performance depends on the hardware and software library.
- Checksums for detecting accidental changes to text, records, or files. Detecting unauthorized changes requires comparison with a trusted or independently protected SHA-512/256 digest.
- Deduplication for identifying records or content that probably contain identical bytes. Applications should still account for the theoretical possibility of a collision.
- Legacy compatibility when an existing file format, API, protocol, or database column explicitly names SHA-512/256.
- Cryptographic protocols that specify this algorithm for digesting data or constructing a supported HMAC.
Do not substitute SHA-256 just because both algorithms return 256 bits. Their digests are different and are identified by different algorithm names. Likewise, SHA-512/224 generator and SHA-512 generator produce different digest lengths, while SHA-3/224 generator belongs to a separate hash family.
How does SHA-512/256 handle spaces and Unicode text?
SHA-512/256 hashes bytes, so spaces, punctuation, numbers, and character encoding all affect the result. This SHA-512/256 generator hashes a number entered as text as its character representation. For example, 42, 042 and 42.0 are unrelated inputs from the algorithm's perspective.
Accented and non-Latin characters must first be encoded as bytes, commonly with UTF-8. Two strings that look alike can produce different hashes if they use different Unicode representations. An accented letter may be stored as one code point or as a base letter followed by a combining mark. Before comparing SHA-512/256 digests from this tool with those from separate systems, normalize the text consistently.
Very long input still produces a 256-bit digest. Empty input also has a defined SHA-512/256 digest, although an empty field in an interface may be treated differently from an intentionally supplied zero-length string. Using the wrong algorithm, different encodings, and ordinary leading or trailing whitespace are common causes of checksum mismatches. Hidden tabs, differences between Windows and Unix line endings, and copied non-breaking spaces can also cause mismatches when present.
Frequently asked questions
Is SHA-512/256 the same as SHA-256?
No. Both return 256-bit digests, but SHA-256 uses a 32-bit internal design, while SHA-512/256 uses the SHA-512 design with its own initial values. The same input produces different output with the two algorithms.
Is SHA-512/256 just a shortened SHA-512 hash?
No. SHA-512/256 starts with different initial hash values, so its output is not the first 256 bits of an ordinary SHA-512 digest. Truncating SHA-512 will therefore fail compatibility checks that require SHA-512/256.
Does the case of hexadecimal letters change the hash?
Uppercase and lowercase hexadecimal text can represent the same SHA-512/256 digest bytes. However, a case-sensitive database or string comparison may treat those written forms as different, so use one agreed-upon format throughout a system.
Can two different inputs have the same SHA-512/256 digest?
Yes, in theory, because an unlimited number of possible inputs are mapped to a fixed number of outputs. Such a pair is called a collision. No practical collision attack is known for SHA-512/256, but applications should not assume mathematical uniqueness.
Can I use SHA-512/256 as a message authentication code?
No, not by placing a secret before the message and hashing the combined text. Use a standard HMAC-SHA-512/256 implementation when authentication with a secret key is required.
Final checks
Before comparing this tool's digest, confirm that the other value uses SHA-512/256, the same input encoding, and the same hexadecimal format. Remove unintended spaces or line breaks, but do not alter text that is meant to contain them. For sensitive input, remember that this tool processes the value on the server over HTTPS, even though the value is not stored.
Popular Tools
Create your own custom signature and download it easily with our signature generator tool for personalized e-signatures.
Calculate the size of any text in Bytes (B), Kilobytes (KB), or Megabytes (MB) using our text size calculator tool.
Use the reverse IP lookup tool to find the domain or host associated with any IP address quickly and easily.
Use our ping tool to check the status and response time of any website, server, or port quickly and efficiently.
Generate your free WhatsApp link instantly with our WhatsApp Link Generator. Add a custom message and start chats in one click. No login or coding required.
Digily Link's IP lookup tool provides detailed information about any IP address. Use this free online service to get comprehensive IP data.