SHA-512 generator
Generate SHA-512 hashes from any string input with our SHA-512 generator tool for high-level data security.
SHA-512 generator is a free tool that converts string input into a fixed-length, 512-bit SHA-512 hash.
What is SHA-512?
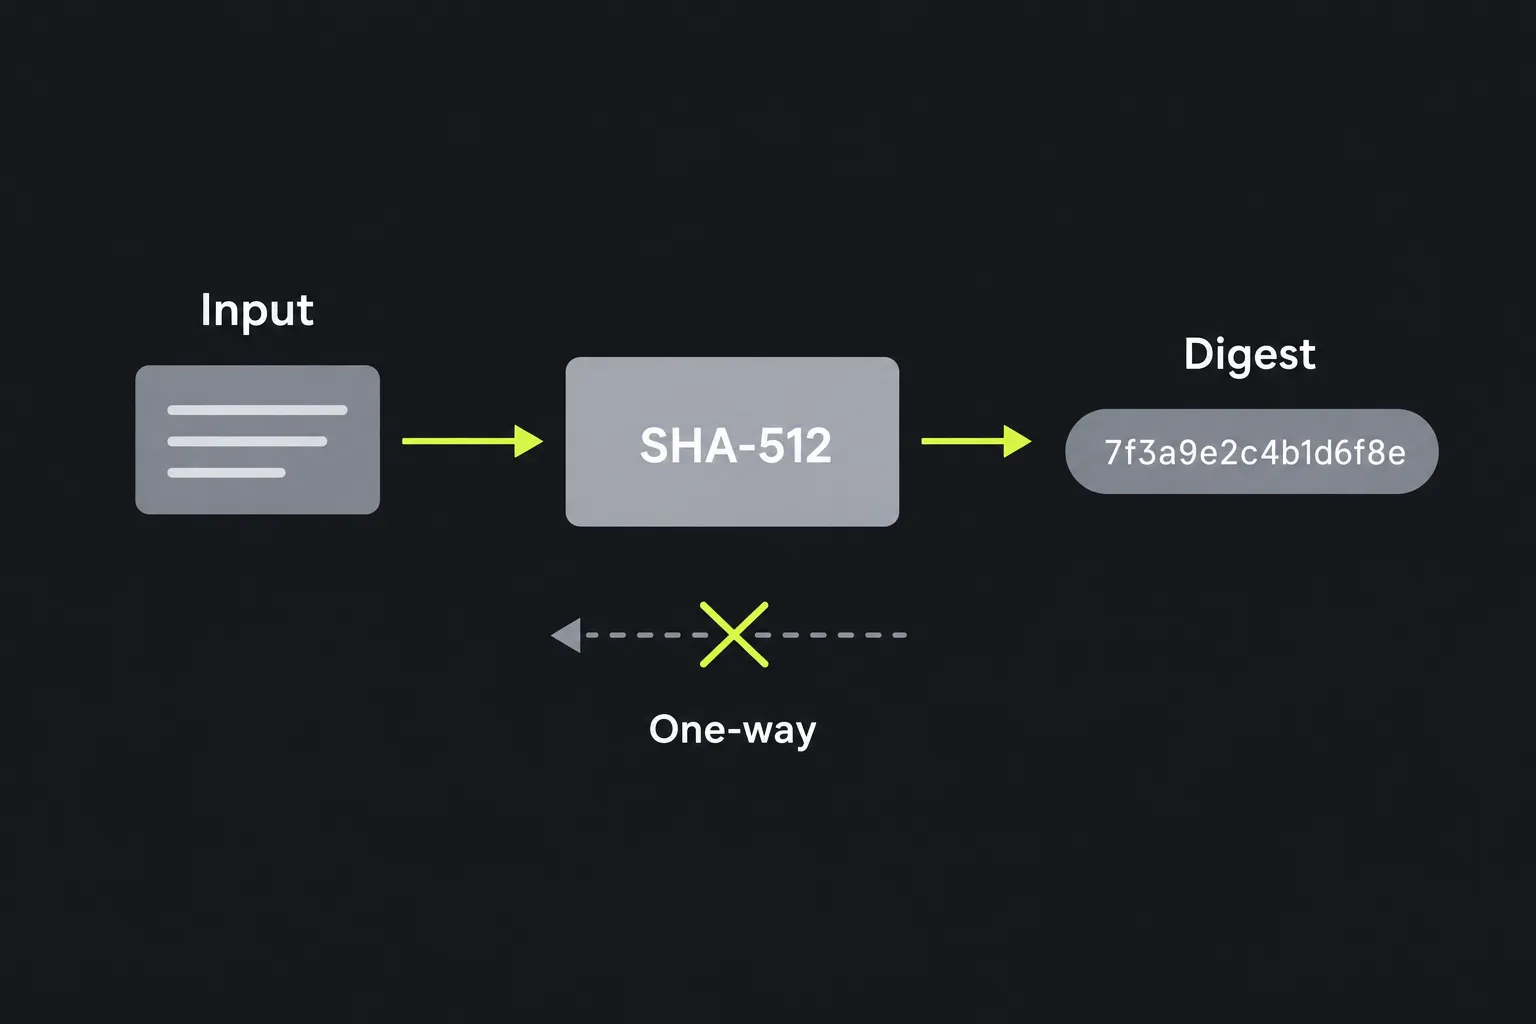
SHA-512 is a cryptographic hash function in the SHA-2 family. It was designed by the U.S. National Security Agency and published by NIST in 2001. It accepts input of varying lengths, processes it in one direction, and returns a fixed-length digest.
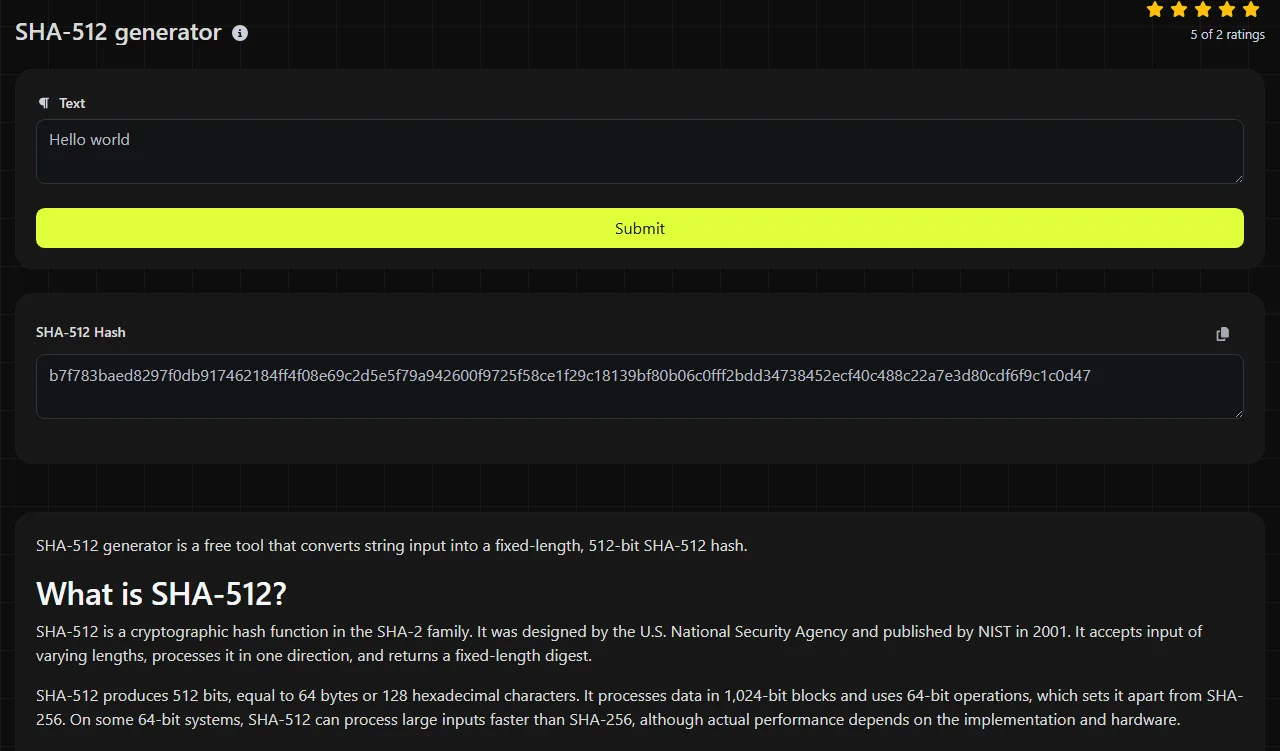
SHA-512 produces 512 bits, equal to 64 bytes or 128 hexadecimal characters. It processes data in 1,024-bit blocks and uses 64-bit operations, which sets it apart from SHA-256. On some 64-bit systems, SHA-512 can process large inputs faster than SHA-256, although actual performance depends on the implementation and hardware.
SHA-512 remains cryptographically secure for general hashing. There is no practical collision attack against the full algorithm, and it has not been deprecated. Because of the birthday bound, its expected collision resistance is about 256 bits. That does not make it suitable for every security task, especially password storage.
How do I use the SHA-512 generator?
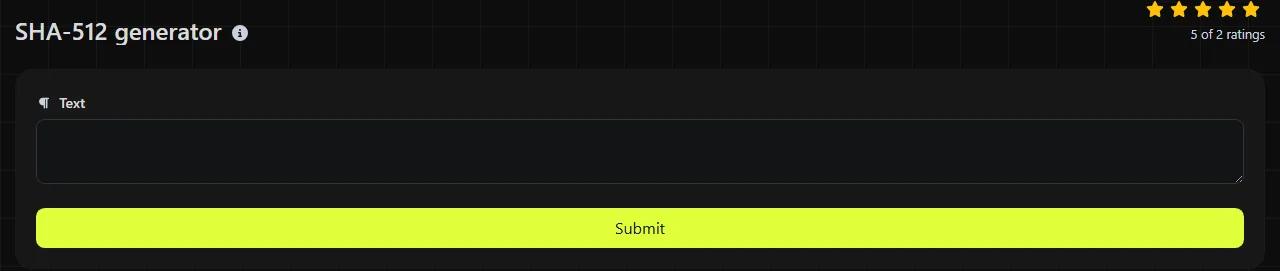
Enter the exact string you want to hash, then read the generated value from the SHA-512 Hash result field. The result should contain 128 hexadecimal characters using the digits 0 through 9 and the letters a through f.
- Copy the source text exactly, including any spaces, punctuation, and line breaks that are part of it.
- Generate the hash and copy the entire result, not a shortened portion.
- Compare it with another SHA-512 digest only if both were created from the same bytes and represented in the same format.
The calculation takes place on the server. Your input is sent to the server over HTTPS and is not stored. Even with HTTPS and no storage, avoid submitting passwords, private keys, recovery codes, or other secrets that do not need to be processed by an online service.
Can SHA-512 be decrypted or reversed?
No. SHA-512 cannot be decrypted because hashing is not encryption, and there is no decryption key. The function discards information as it produces its fixed-length result, so the original value cannot be reconstructed directly from the digest.
An attacker can still guess possible inputs, hash each guess, and compare the results. This works against short, common, or predictable values such as dictionary words, phone numbers, and reused passwords. Online hash databases may also contain previously calculated hashes for common strings. A hash therefore does not make weak input secret.
Different inputs can theoretically produce the same digest, which is known as a collision. With full SHA-512, finding such a collision is beyond practical reach using known methods. This security property does not change the fact that guessable input can be discovered through repeated testing.
Where should SHA-512 be used today?
SHA-512 is appropriate when a system or specification requires a full 512-bit SHA-2 digest. Common legitimate uses include checking whether data has changed, identifying duplicate content, and maintaining compatibility with existing formats or software.
- Checksums can confirm that a downloaded or transferred item matches a separately published SHA-512 value. A checksum alone does not prove who published the data.
- Deduplication systems can use a digest as a compact content identifier, although systems that handle hostile input should still confirm matches when necessary.
- Legacy compatibility may require SHA-512 when an existing database column, API, or exchange format already expects 128 hexadecimal characters.
- Digital signatures and authentication protocols may use SHA-512 as one component of a defined cryptographic construction.
Do not use plain SHA-512 to store passwords. It is intentionally fast to calculate, allowing an attacker to test guesses at high speed. Use a password-hashing function such as Argon2id, scrypt, bcrypt, or PBKDF2 with appropriate settings and a unique salt.
Choose SHA-256 when compatibility or a shorter 64-character digest matters. Use the SHA-384 generator when a protocol explicitly requires SHA-384. SHA-512/224 is a separately defined algorithm with a 224-bit result, not simply an informal shortening of a SHA-512 string.
Input details and worked examples
SHA-512 hashes bytes, so every input detail matters. Uppercase letters, trailing spaces, punctuation, and line endings all change the byte sequence and normally produce a completely different digest. The text Invoice 42 and Invoice 42 , with a final space in the second version, are different inputs.
For the ASCII input abc, the standard SHA-512 result is:
ddaf35a193617abacc417349ae20413112e6fa4e89a97ea20a9eeee64b55d39a2192992a274fc1a836ba3c23a3feebbd454d4423643ce80e2a9ac94fa54ca49f
Numbers entered in a text field are treated as characters. For example, 0123 differs from 123 because the leading zero is part of the string. Accented and non-Latin text also has a valid hash, but character encoding and Unicode normalization affect the bytes. Two visually identical strings can therefore produce different values if one uses a composed character and the other uses combining marks.
The SHA-512 algorithm defines a digest for an empty byte sequence and can process very long messages. A web interface may have practical request or server limits, so use a local hashing command for very large files or data that should not be transmitted.
Frequently asked questions
Does uppercase hexadecimal change a SHA-512 hash?
No. Uppercase and lowercase hexadecimal are two representations of the same digest, so AF and af represent the same byte value. Letter case in the original input does matter.
Can I use this generator to calculate a file checksum?
No. This tool is designed for string input and does not provide a file result field. Pasting file contents can alter binary data or line endings. For files, use a local command such as sha512sum on Linux or Get-FileHash -Algorithm SHA512 in PowerShell.
Is SHA-512 safe for message authentication?
No. Plain SHA-512 does not authenticate a message because anyone can calculate a new digest after changing the content. A naive secret-prefix construction can also be affected by SHA-512's length-extension property. Use HMAC-SHA-512 when a shared secret must authenticate the message.
Does adding a salt make SHA-512 suitable for passwords?
No. A salt prevents identical passwords from sharing the same stored value, but it does not make a fast general-purpose hash expensive enough for password guessing. Use a dedicated password-hashing function and store its algorithm identifier, salt, and cost settings with the result.
Why is my SHA-512 value different from one generated by another website or program?
Check for hidden spaces, a final line break, different character encoding, or a copied byte-order mark. Also confirm that the other program produced full SHA-512 rather than SHA-384, SHA-512/224, HMAC-SHA-512, or Base64-encoded output. Compare the input as bytes when an exact match is required.
Popular Tools
Create your own custom signature and download it easily with our signature generator tool for personalized e-signatures.
Calculate the size of any text in Bytes (B), Kilobytes (KB), or Megabytes (MB) using our text size calculator tool.
Use the reverse IP lookup tool to find the domain or host associated with any IP address quickly and easily.
Use our ping tool to check the status and response time of any website, server, or port quickly and efficiently.
Generate your free WhatsApp link instantly with our WhatsApp Link Generator. Add a custom message and start chats in one click. No login or coding required.
Digily Link's IP lookup tool provides detailed information about any IP address. Use this free online service to get comprehensive IP data.