SHA-3/224 generator
Generate SHA-3/224 hashes from any string input with our SHA-3/224 generator tool for strong data encryption.
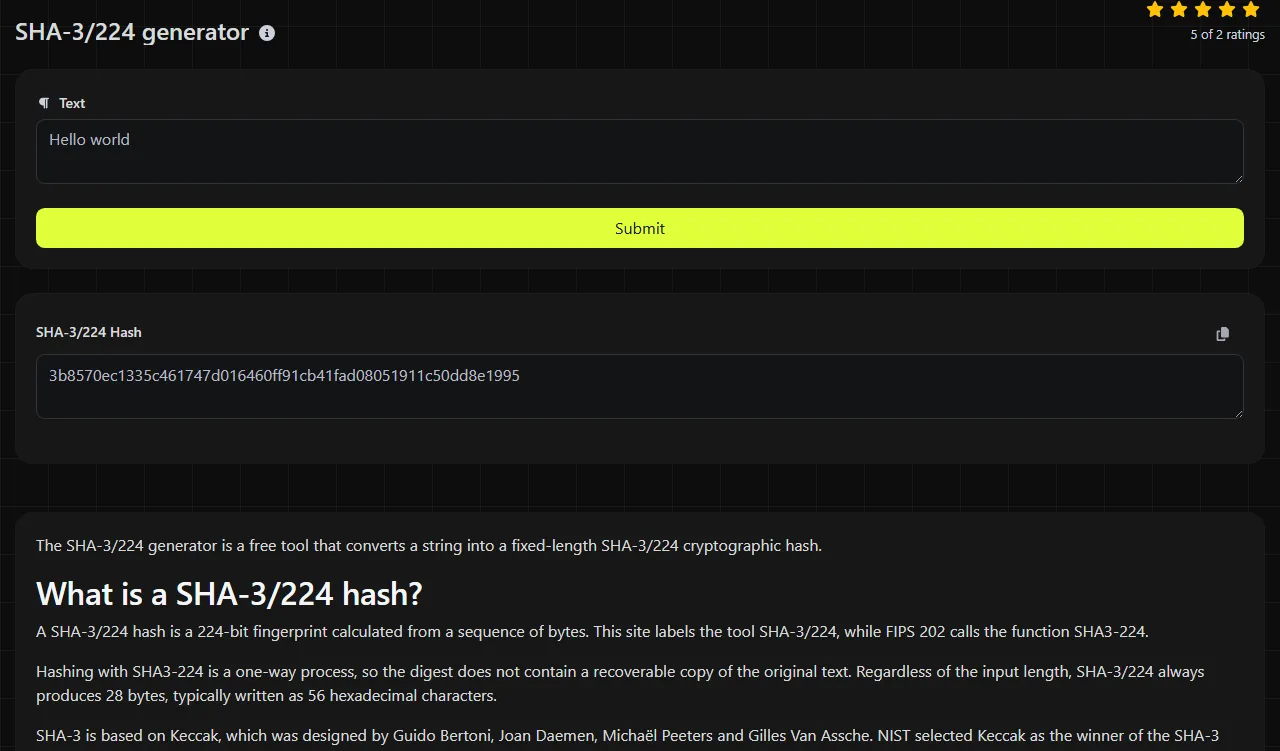
The SHA-3/224 generator is a free tool that converts a string into a fixed-length SHA-3/224 cryptographic hash.
What is a SHA-3/224 hash?
A SHA-3/224 hash is a 224-bit fingerprint calculated from a sequence of bytes. This site labels the tool SHA-3/224, while FIPS 202 calls the function SHA3-224.
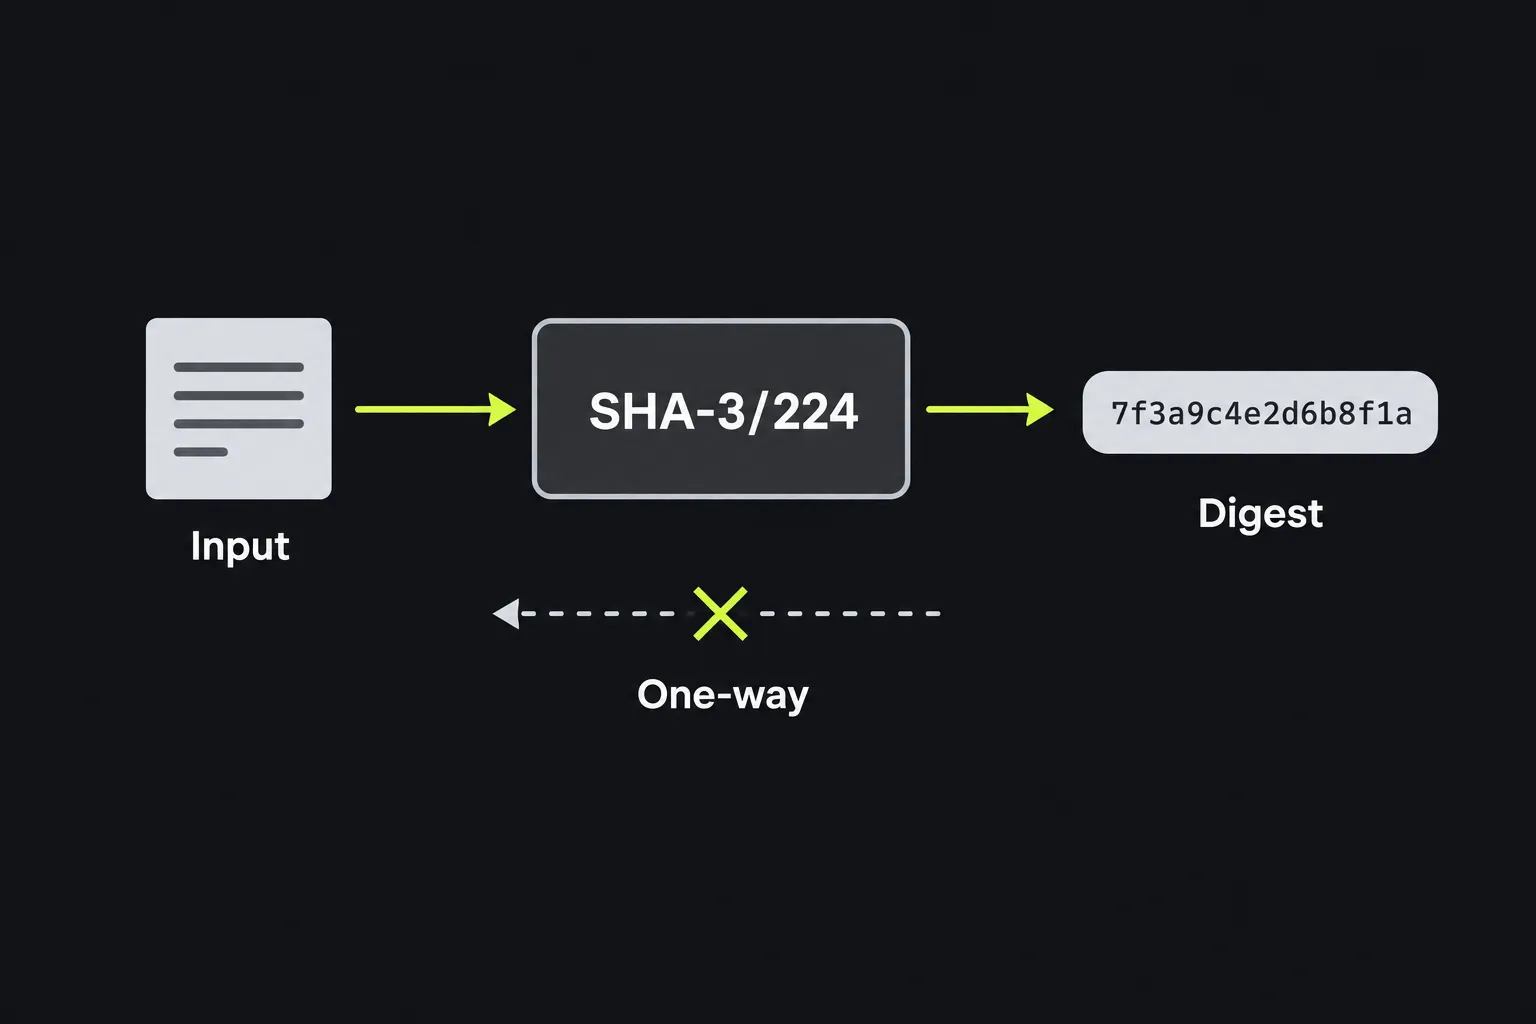
Hashing with SHA3-224 is a one-way process, so the digest does not contain a recoverable copy of the original text. Regardless of the input length, SHA-3/224 always produces 28 bytes, typically written as 56 hexadecimal characters.
SHA-3 is based on Keccak, which was designed by Guido Bertoni, Joan Daemen, Michaël Peeters and Gilles Van Assche. NIST selected Keccak as the winner of the SHA-3 competition in 2012 and published the SHA-3 standard in 2015. SHA3-224 uses a sponge construction, which differs from the construction used by SHA-2.
SHA-3/224 is still considered secure for general-purpose hashing. There are no known practical attacks that break the full algorithm. Its 224-bit output provides about 112 bits of collision resistance because collision attacks generally require roughly the square root of the possible output space. Applications that need a larger security margin commonly choose SHA-3/256 instead.
How do I use the SHA-3/224 generator?
Enter the exact string you want to hash, then generate the result. The tool returns a SHA-3/224 Hash containing 56 hexadecimal characters.
The calculation takes place on the server. Your input is sent to the server over HTTPS and is not stored. Although HTTPS protects the connection while the data is in transit, avoid submitting passwords, private keys, recovery phrases or other secrets to an online hashing tool.
When comparing the 56-character SHA3-224 result with an expected checksum, copy the entire digest. A single missing character changes the value and makes the comparison invalid.
Can SHA-3/224 be decrypted or reversed?
No. A SHA-3/224 hash cannot be decrypted because hashing is not encryption, and there is no decryption key. The only general way to identify an unknown input from its SHA3-224 digest is to try possible values, hash each one and compare the results.
This distinction matters for short or predictable inputs hashed with SHA3-224. An attacker may guess a ZIP code, common password or six-digit code even though the algorithm itself has not been reversed. A SHA3-224 hash therefore does not make low-entropy data secret.
Collisions are theoretically possible because an unlimited number of inputs are mapped to a finite 224-bit space. Finding a collision for the full SHA-3/224 algorithm is not currently practical, but that does not make the digest a form of encrypted storage.
When should I use SHA-3/224?
Use SHA-3/224 when a specification, existing system or provided checksum explicitly requires that variant. Its shorter digest can suit formats with a fixed 224-bit field, but it is less common than SHA-3/256.
- SHA3-224 checksum verification means calculating a digest and comparing it with a value published by a trusted source.
- Deduplication means identifying matching records or content without repeatedly comparing the entire input. Applications that use SHA3-224 should still account for the theoretical possibility of a collision.
- Legacy compatibility applies when an existing database, protocol or integration already stores SHA-3/224 values.
- Test fixtures can use known inputs and digests to verify that another SHA3-224 implementation is configured correctly.
Do not use SHA-3/224 to store passwords. SHA3-224 is intentionally fast, which also allows an attacker to test guesses quickly. Password storage requires a dedicated, slow password-hashing scheme such as Argon2id, scrypt, bcrypt or PBKDF2 with appropriate parameters and a unique salt.
For a new general-purpose checksum format, SHA-3/256 provides a longer digest and is more commonly selected. The SHA-3/256 generator is appropriate when no external requirement fixes the output at 224 bits. SHA-512/224 has the same digest length but belongs to the SHA-2 family, so its output is not interchangeable with SHA-3/224.
Exact input and worked examples
For this generator's string input, SHA3-224 processes bytes, so every character and its encoding matter. Two strings that look similar can produce unrelated SHA3-224 digests.
- The input invoice produces a 56-character hexadecimal digest.
- The input Invoice produces a different digest because uppercase and lowercase letters are different bytes.
- The inputs order 42 and order42 differ because the space is part of the data.
- Punctuation and line endings count in this generator's input. paid, paid. and a line containing paid followed by a newline all produce different hashes.
- An empty input has a valid SHA-3/224 digest. It does not produce an empty result.
- Numbers are hashed as encoded text when they are submitted to this generator as a string. 007 and 7 are different inputs.
To reproduce the bytes submitted to this server-side SHA3-224 generator, accented and non-Latin text must use the same character encoding in every system, normally UTF-8. Unicode can also represent some visible characters with more than one byte sequence. If another application normalizes text before hashing, both sides must use the same normalization form.
Input length does not change the output length. Even a very long string produces 56 hexadecimal characters, although processing and transmitting it takes more time than handling a short string.
Frequently asked questions
Are SHA-3/224 and SHA-224 the same?
No. SHA-224 is a SHA-2 variant, while SHA-3/224 uses the Keccak-based SHA-3 construction. Both produce 224-bit digests, but they generate completely different values from the same input.
Does uppercase hexadecimal change the hash?
No. In this tool's SHA-3/224 Hash field, uppercase and lowercase hexadecimal are alternative written forms of the same digest bytes. A comparison may still fail if the software treats the text as case-sensitive, so normalize both values to the same case before comparing them.
Is SHA-3/224 vulnerable to length-extension attacks?
No. Standard SHA-3 hashes are not vulnerable to the classic length-extension attack that affects certain Merkle-Damgård hashes. SHA3-224's resistance to this attack does not mean that a plain hash is always an appropriate message authentication code. Use a specified MAC construction when authentication is required.
Can I compare SHA-3/224 results from different programming languages?
Yes. Implementations that conform to the formal SHA3-224 algorithm produce the same digest from identical bytes. For this generator's string input, check the character encoding, newline convention and whether either implementation hashes a textual hexadecimal representation instead of the underlying bytes.
Can this generator hash an uploaded file?
No. The tool is specified for string input, so do not assume it reads file bytes directly. To calculate a file checksum, use a file-aware hashing utility or command-line implementation and explicitly select SHA3-224.
Final checks
Confirm that the required algorithm is SHA-3/224, not SHA-224, SHA-512/224 or SHA-3/256. Preserve spaces, punctuation, capitalization and line endings, then verify that the result contains exactly 56 hexadecimal characters. For repeatable checks across systems, record the input encoding and any Unicode normalization applied before hashing.
Popular Tools
Create your own custom signature and download it easily with our signature generator tool for personalized e-signatures.
Calculate the size of any text in Bytes (B), Kilobytes (KB), or Megabytes (MB) using our text size calculator tool.
Use the reverse IP lookup tool to find the domain or host associated with any IP address quickly and easily.
Use our ping tool to check the status and response time of any website, server, or port quickly and efficiently.
Generate your free WhatsApp link instantly with our WhatsApp Link Generator. Add a custom message and start chats in one click. No login or coding required.
Digily Link's IP lookup tool provides detailed information about any IP address. Use this free online service to get comprehensive IP data.