SHA-512/224 generator
Generate SHA-512/224 hashes from any string input with our SHA-512/224 generator tool for enhanced data security.
The SHA-512/224 generator is a free tool that produces a 224-bit SHA-512/224 hash from any string input.
What is SHA-512/224?
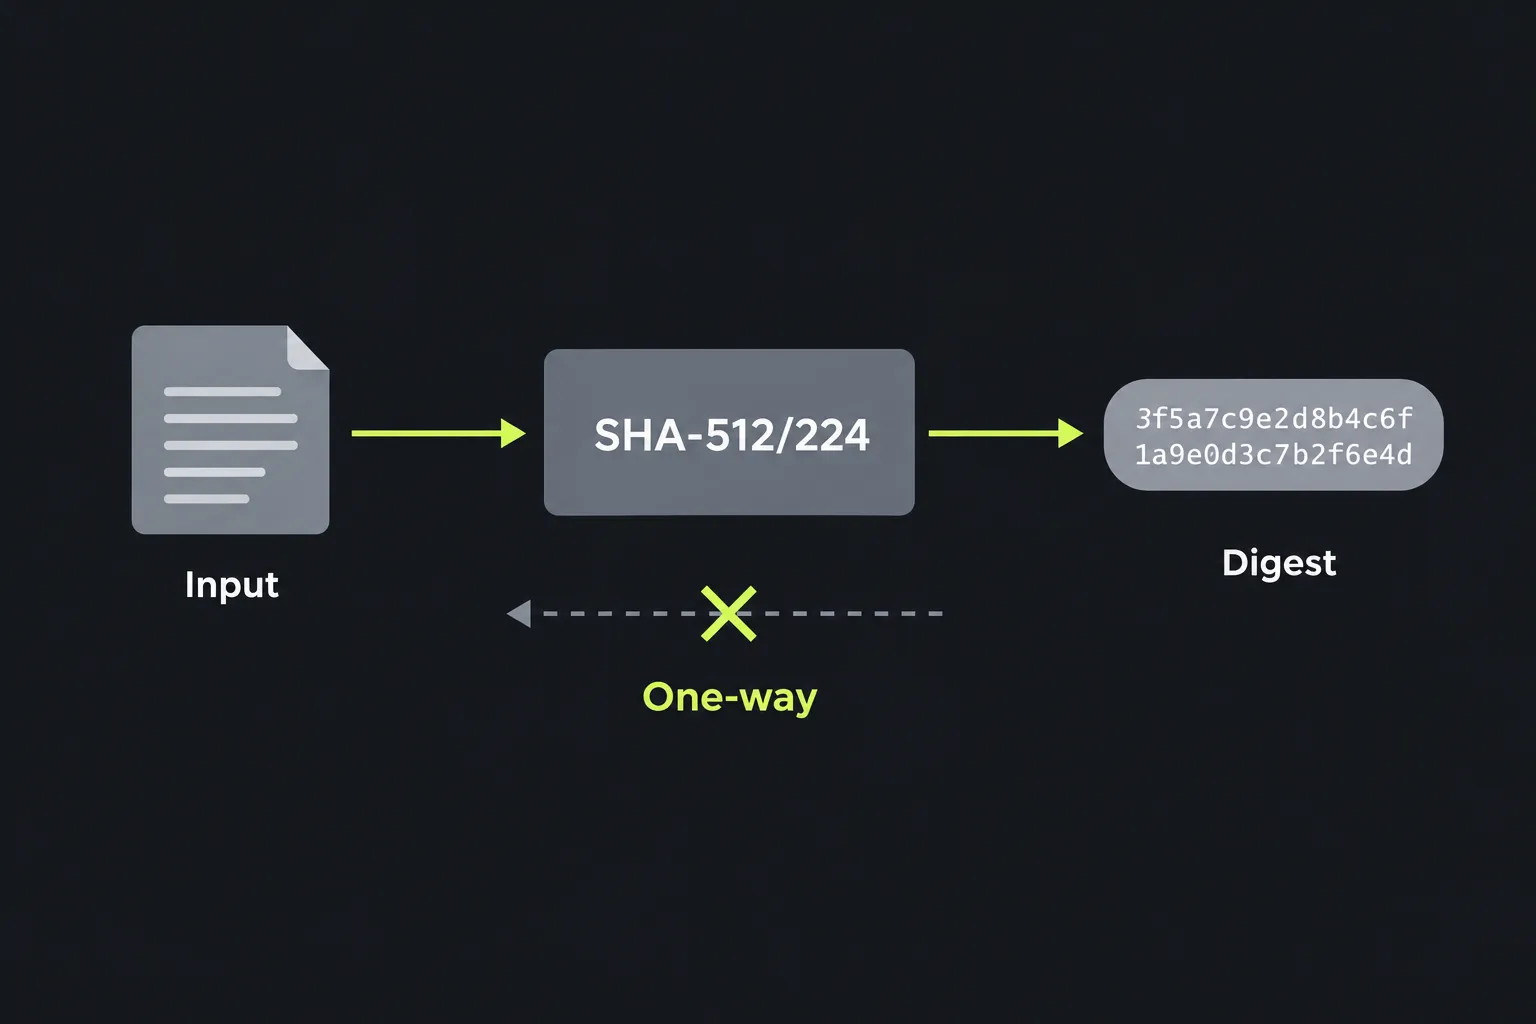
SHA-512/224 is part of the SHA-2 family. It converts input data into a fixed-length fingerprint using a one-way mathematical operation. The same sequence of bytes always produces the same SHA-512/224 digest, while even a small change usually produces a very different result. SHA-512/224 is not encryption because it has no decryption key and is not designed to recover the original data.
The algorithm uses SHA-512's internal structure, including 64-bit operations and 1,024-bit message blocks, but produces a 224-bit digest. That equals 28 bytes and is usually displayed as 56 hexadecimal characters.
SHA-2 was designed by the U.S. National Security Agency and first standardized by NIST in 2002. The SHA-512/224 variant was specified in FIPS 180-4 in 2012. It remains an accepted SHA-2 algorithm and has no known practical break, although its 224-bit output provides about 112 bits of theoretical collision resistance.
How do I generate a SHA-512/224 hash?
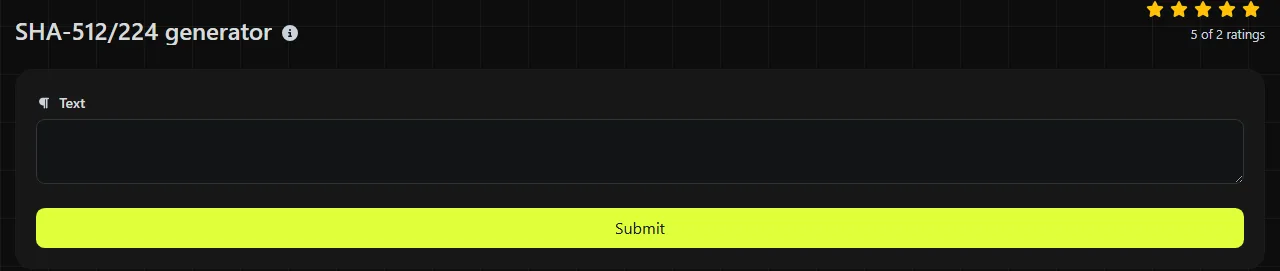
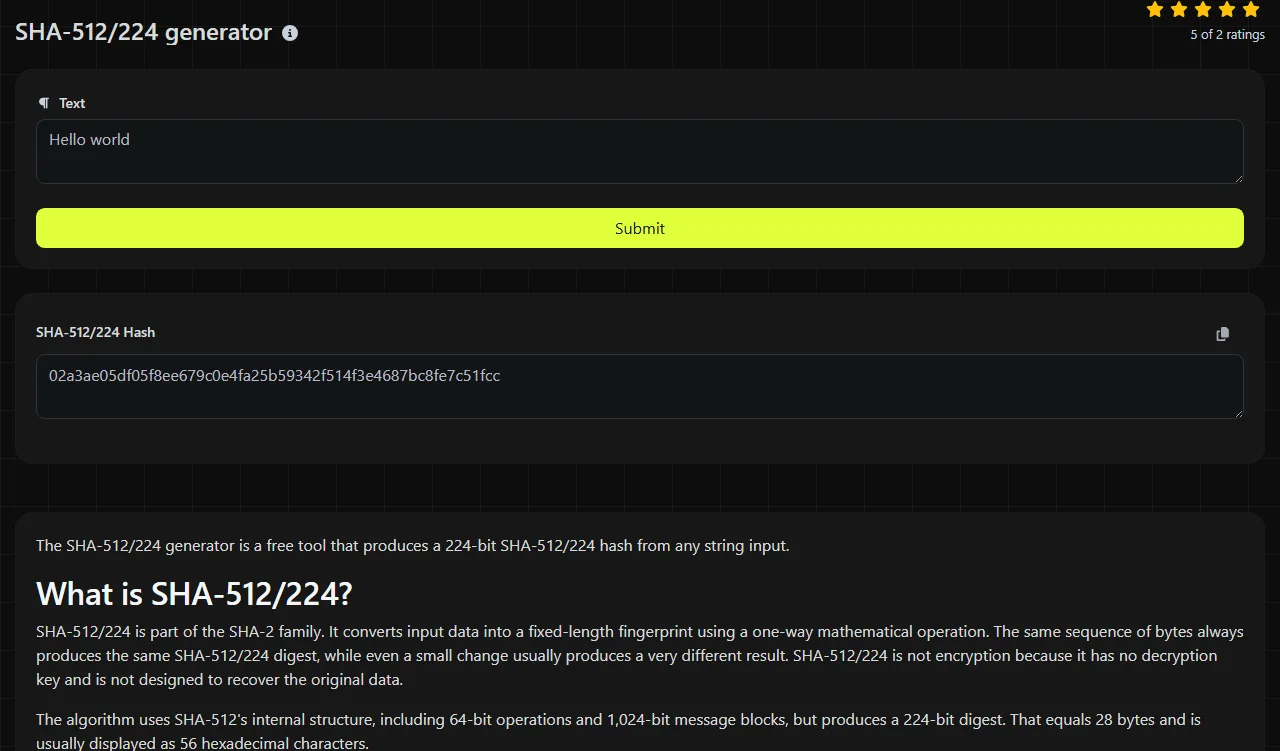
Enter the string you want to hash, then read the generated value in the SHA-512/224 Hash result field. The output contains 56 hexadecimal characters, using the digits 0 through 9 and the letters a through f.
For example, the input invoice-2026-0041 produces one 224-bit digest. Changing the final digit to invoice-2026-0042 produces a different SHA-512/224 digest of exactly the same length. A long paragraph and a single letter also produce SHA-512/224 outputs of the same length.
SHA-512/224 generation takes place on the server. The string you enter in this generator is sent to the server over HTTPS and is not stored. Do not submit passwords, private keys, access tokens, or other secrets to this generator just to check their hashes, since the input still leaves your device during processing.
This SHA-512/224 generator hashes the bytes representing the submitted string, so spaces, letter case, punctuation, line breaks, and tab characters affect the result. Numbers are hashed as characters, so the strings 7 and 07 differ. Accented and non-Latin text can have distinct Unicode representations even when it looks identical on screen. SHA-512/224 also defines a digest for the empty byte string.
Can SHA-512/224 be decrypted or reversed?
No. SHA-512/224 cannot be decrypted because hashing is not an encryption process. There is no key or built-in reverse operation that converts a digest back into its original string.
The 224-bit output does not prevent an attacker from hashing possible inputs and comparing each result with a SHA-512/224 digest. Predictable values such as common passwords, short PINs, or small lists of reference numbers therefore remain vulnerable to guessing.
Two different inputs could theoretically produce the same digest, which is known as a collision. SHA-512/224's 224-bit output means collision searches have a theoretical security level of about 112 bits. No practical collision attack against SHA-512/224 is currently known.
Legitimate uses and security limits
SHA-512/224 is suitable when a system specifically requires this algorithm or when a compact SHA-2 digest is useful. Its less common format can limit compatibility, so confirm the required algorithm name and digest length before exchanging values with another service.
- Checksums using SHA-512/224 can reveal accidental changes to text or records, provided the expected hash comes from a reliable source.
- Deduplication can use SHA-512/224 digests as an initial way to identify likely duplicate string content, followed by a direct comparison when a collision would matter.
- Legacy compatibility may require SHA-512/224 when working with an existing protocol, database field, or software implementation.
- Content identifiers can represent stable byte sequences in systems where 224-bit identifiers are part of the agreed-upon format.
Do not use a plain SHA-512/224 digest to store passwords. It is designed to run quickly, which also allows attackers to test guesses quickly. Instead of this generator, use a dedicated password-hashing scheme such as Argon2id, bcrypt, scrypt, or PBKDF2 for password storage, with an individual salt and appropriate cost settings.
A SHA-512/224 digest from this generator does not prove who created the input string. If an attacker can replace both the string and its digest, the check provides no authentication. Use a digital signature or an HMAC construction when authenticity matters.
Should I choose SHA-512/224, SHA-512/256, or SHA-384?
Choose SHA-512/224 only when a specification requires it or when its 224-bit output is an intentional compatibility choice. It is not simply SHA-512 with the displayed result cut to 224 bits. The standard defines a distinct initial state to separate it from ordinary truncated SHA-512.
SHA-512/256 produces a 256-bit digest, providing about 128 bits of theoretical collision resistance, and should be chosen when a specification requires its 256-bit output. SHA-384 produces a 384-bit digest and is widely used in established security protocols. The SHA-512 generator returns the full 512-bit result when truncation is neither required nor desirable.
Compatibility requirements usually determine whether you should choose SHA-512/224, SHA-512/256, SHA-384, or SHA-512. A SHA-512/224 digest can be compared only when both sides use SHA-512/224, the same byte encoding, and the exact same input.
Frequently asked questions
Is SHA-512/224 the same as SHA-224?
No. SHA-224 uses the SHA-256 internal structure, while SHA-512/224 uses the SHA-512 structure with different initial values and a 224-bit result. Both produce 56 hexadecimal characters, but their digests for the same input are different.
Does letter case matter in a hexadecimal hash?
No. Uppercase and lowercase hexadecimal letters represent the same numeric digest, so ab and AB are equivalent within a displayed hash. Letter case does matter in the string submitted to this SHA-512/224 generator.
Can I use SHA-512/224 as a message authentication code?
Do not create one by simply placing a secret before or after the message. SHA-512-family hashes have structural properties that make improvised keyed schemes unsafe. Use HMAC-SHA-512/224 instead when that algorithm has been agreed upon.
Why do two strings that look identical produce different hashes?
They may contain hidden spaces, different line endings, or distinct Unicode representations. For example, an accented letter can be stored as one code point or as a base letter followed by a combining mark. Before comparing results from this SHA-512/224 generator across different systems, normalize the text and encoding.
Can I compare a SHA-512/224 hash with a SHA-512 hash?
No. Truncating a standard SHA-512 digest to 56 hexadecimal characters does not create a SHA-512/224 digest because the algorithms start from different initial values. Confirm that both systems explicitly specify SHA-512/224 before relying on a comparison.
Popular Tools
Create your own custom signature and download it easily with our signature generator tool for personalized e-signatures.
Calculate the size of any text in Bytes (B), Kilobytes (KB), or Megabytes (MB) using our text size calculator tool.
Use the reverse IP lookup tool to find the domain or host associated with any IP address quickly and easily.
Use our ping tool to check the status and response time of any website, server, or port quickly and efficiently.
Generate your free WhatsApp link instantly with our WhatsApp Link Generator. Add a custom message and start chats in one click. No login or coding required.
Digily Link's IP lookup tool provides detailed information about any IP address. Use this free online service to get comprehensive IP data.