Whirlpool generator
Create whirlpool hashes from any string input using our whirlpool generator tool for robust data encryption.
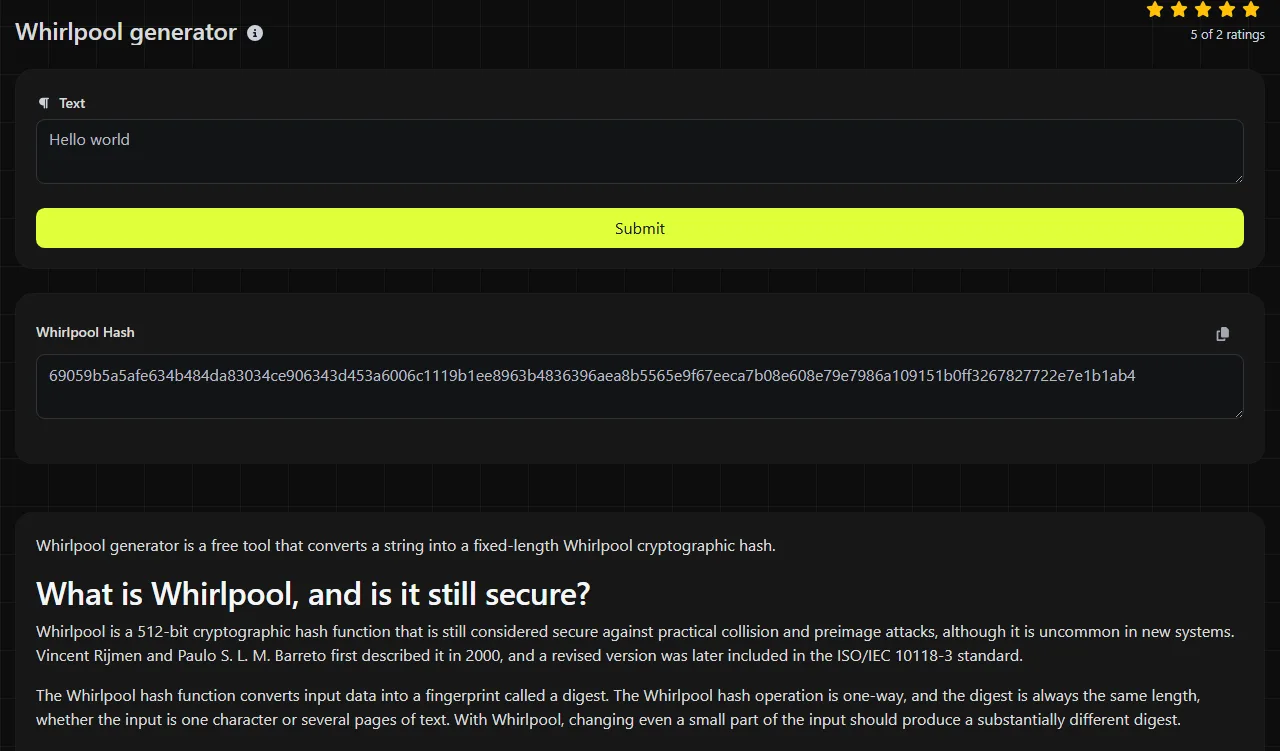
Whirlpool generator is a free tool that converts a string into a fixed-length Whirlpool cryptographic hash.
What is Whirlpool, and is it still secure?
Whirlpool is a 512-bit cryptographic hash function that is still considered secure against practical collision and preimage attacks, although it is uncommon in new systems. Vincent Rijmen and Paulo S. L. M. Barreto first described it in 2000, and a revised version was later included in the ISO/IEC 10118-3 standard.
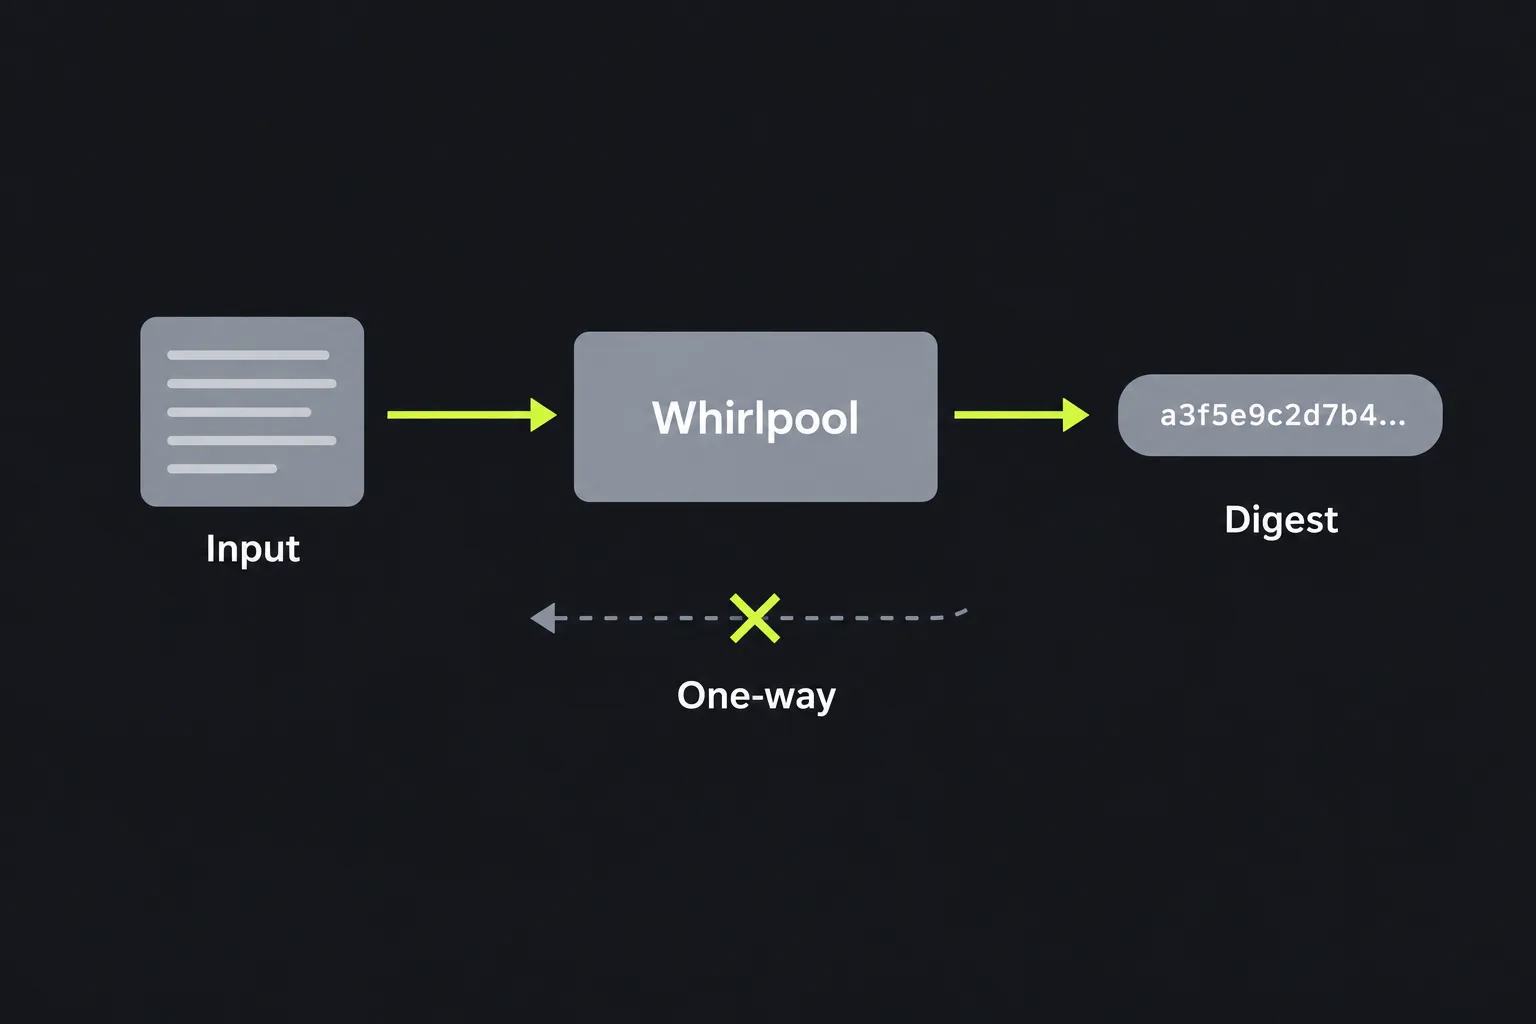
The Whirlpool hash function converts input data into a fingerprint called a digest. The Whirlpool hash operation is one-way, and the digest is always the same length, whether the input is one character or several pages of text. With Whirlpool, changing even a small part of the input should produce a substantially different digest.
Whirlpool produces 512 bits, or 64 bytes. When displayed in hexadecimal, a digest contains 128 hexadecimal characters. The full algorithm has no known practical break, but its limited adoption means SHA-256 or SHA-512 is usually easier to integrate with current software and protocols.
How do I use the Whirlpool generator?
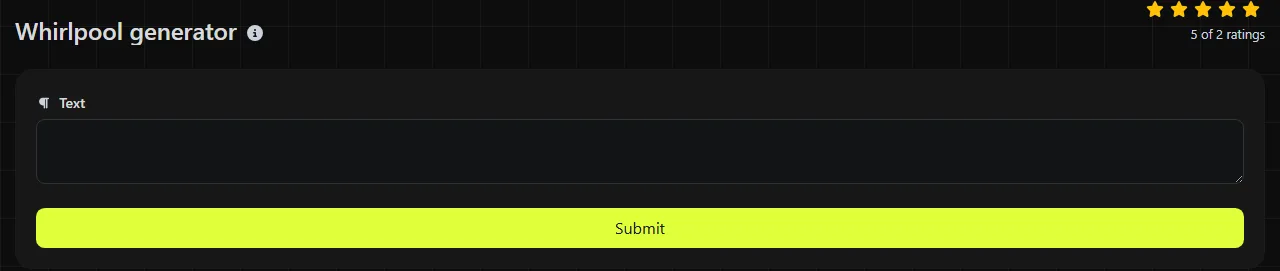
Enter the exact string you want to hash, then use the value shown in the Whirlpool Hash result field. Copy the entire Whirlpool digest without adding or removing any characters.
The Whirlpool calculation takes place on the server. Your input to this Whirlpool generator is sent to the server over HTTPS and is not stored. Because it leaves your device during processing, avoid submitting passwords, private keys, or other material that must never be sent to an external service.
A conventional hexadecimal result has this form:
- Entering invoice-2026 produces a 512-bit digest displayed as 128 hexadecimal characters.
- Entering Invoice-2026 produces a different 128-character digest because the capital letter changes the input.
- Entering invoice-2026 also produces a different digest because the trailing space is part of the string.
When checking a known value, make sure both sides use Whirlpool rather than another 512-bit algorithm. A 128-character digest alone does not identify Whirlpool.
Can a Whirlpool hash be decrypted or reversed?
No. A Whirlpool hash cannot be decrypted because hashing is not encryption and does not have a decryption key. Someone can only try possible inputs, hash each one, and look for a matching digest.
This guessing process may recover short or predictable input. A hash of a common word can be found by testing dictionaries or previously calculated values, even though the hash function itself has not been reversed. Longer, unpredictable input is much harder to guess, but that does not make raw Whirlpool suitable for password storage.
Password databases should use a password-hashing scheme such as Argon2id, scrypt, or bcrypt instead of raw Whirlpool. These schemes support salts and deliberately expensive processing, which slows large-scale guessing. Whirlpool is a general-purpose hash and does not provide those password-specific protections on its own.
Where Whirlpool still fits
Whirlpool remains useful when an existing specification, archive, or application explicitly requires it. Its 512-bit digest also makes accidental matches extremely unlikely, but compatibility should usually determine whether to use it.
- Checksums can reveal accidental changes to downloads, backups, and transferred data when a trusted Whirlpool value is already available.
- Deduplication systems can use digests as candidate identifiers, followed by a byte-for-byte comparison before deleting data.
- Legacy compatibility may require Whirlpool for older archives, integrity catalogs, or applications that already store its digests.
- Data indexing can use a digest as a fixed-length identifier when the system already standardizes on Whirlpool.
A plain Whirlpool checksum does not prove who created a file. An attacker who can replace both the file and its published hash can make them match, so authenticated systems need a digital signature or a keyed message authentication code.
Do not choose MD2, MD4, or SHA-1 as security upgrades. Those older algorithms are broken for collision resistance. The MD2 generator, MD4 generator, and SHA-1 generator are mainly relevant when reproducing values required by legacy systems.
What input details change a Whirlpool hash?
Whirlpool processes every input byte, including spaces, punctuation, capitalization, and line endings. As a result, two strings that look similar on screen may have different hashes.
- Leading and trailing spaces are part of the input to Whirlpool unless they are removed before hashing.
- For Whirlpool, a line ending written as LF is different input from the CRLF convention commonly used by Windows software.
- Accented and non-Latin characters must be converted to bytes using a character encoding. UTF-8 and another encoding will not necessarily produce the same digest.
- Numbers entered into this Whirlpool generator are treated as characters. The text 0015 differs from 15.
- An empty input still has a defined Whirlpool digest. It is not represented by a blank result.
- Very long input still produces 512 bits.
For repeatable results, preserve the original encoding and line endings, and avoid automatic trimming or Unicode normalization. The algorithm hashes bytes and does not know that two differently encoded sequences may represent the same visible text.
Frequently asked questions
Does uppercase hexadecimal change the hash?
No. In a Whirlpool digest, hexadecimal letters can be written in uppercase or lowercase without changing the underlying digest. If two valid hexadecimal values differ only in letter case, they represent the same bytes.
Does a 512-bit digest provide 512-bit collision security?
No. For an ideal 512-bit hash, generic collision resistance is approximately 256 bits because of the birthday bound. Generic preimage resistance is approximately 512 bits, although those figures do not make up for weak input or poor application design.
Can I use this generator to hash a file?
No. This tool is specified for string input, so arbitrary file bytes should not be pasted into a text field. Use a file-aware local application or library that explicitly supports Whirlpool, then compare the complete 128-character hexadecimal digest.
Should I add a salt to a Whirlpool checksum?
Usually not. Checksums must be reproducible from the original data, while a random salt changes the result and must be retained to reproduce it. Salts are mainly part of password-hashing designs, where Whirlpool alone is not the appropriate choice.
Before relying on a result, check the algorithm name, input encoding, whitespace, and full digest length. Keep the expected checksum in a trusted location separate from the data it is meant to verify.
Popular Tools
Create your own custom signature and download it easily with our signature generator tool for personalized e-signatures.
Calculate the size of any text in Bytes (B), Kilobytes (KB), or Megabytes (MB) using our text size calculator tool.
Use the reverse IP lookup tool to find the domain or host associated with any IP address quickly and easily.
Use our ping tool to check the status and response time of any website, server, or port quickly and efficiently.
Generate your free WhatsApp link instantly with our WhatsApp Link Generator. Add a custom message and start chats in one click. No login or coding required.
Digily Link's IP lookup tool provides detailed information about any IP address. Use this free online service to get comprehensive IP data.